Software Security
About This Service
We embed security into your development process, from threat modeling and secure design to code review and automated security testing in your CI/CD pipeline.
Key Benefits
Shift-Left Security
Integrate security early in the development lifecycle to reduce costs and catch vulnerabilities before production.
Secure Code Review
Expert manual and automated code review to identify security flaws in application source code.
DevSecOps Integration
Automate security testing within your CI/CD pipeline for continuous security validation.
Developer Training
Equip your development team with secure coding knowledge and best practices.
Secure Code Review
Thorough manual and automated review of application source code to identify security vulnerabilities, logic flaws, and insecure coding patterns.
Threat Modeling
Systematic identification of threats and attack vectors during the design phase to build security into applications from the start.
DevSecOps Implementation
Integration of security tools and practices into your CI/CD pipeline for automated security testing, dependency scanning, and container security.
API Security Testing
Comprehensive security testing of REST, GraphQL, and SOAP APIs covering authentication, authorization, data validation, and rate limiting.
Have Questions About Our Security Services?
Get in touch with our team of cybersecurity experts. We're here to help you understand your security needs and find the right solution for your organization.
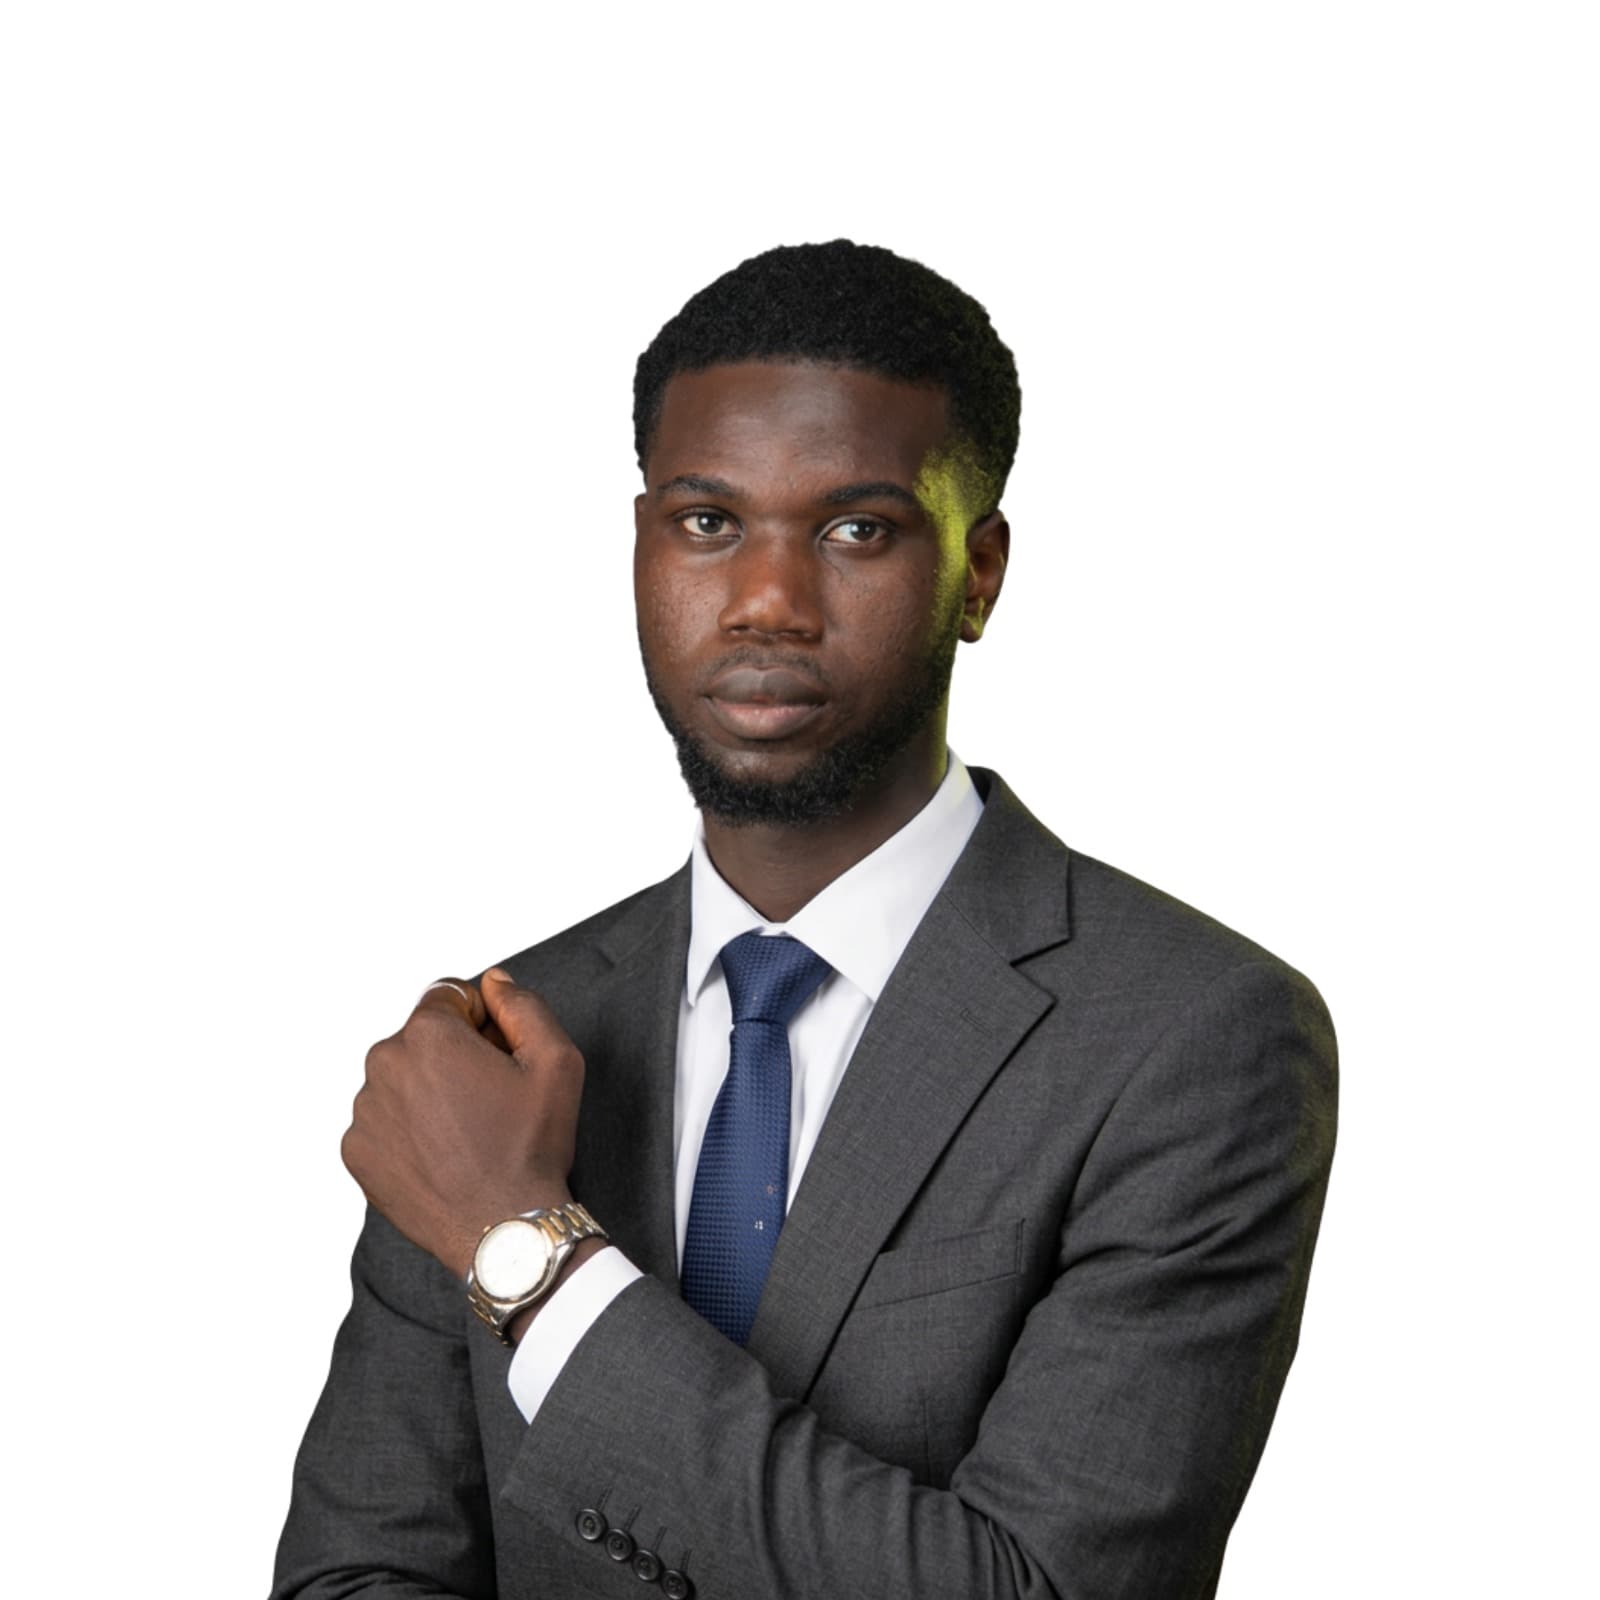
Nwachukwu Francis O.
Founder / Tech Lead
Intelligence behind every decision
Design
Threat model your application architecture and define security requirements.
Develop
Implement secure coding practices with integrated code review and security testing.
Deploy
Validate security through penetration testing and establish ongoing monitoring.
Know your risk. Strengthen what matters.
Tell us where you are, what you rely on, and what you need to protect. We will help you understand what to do next.